Threat Index: what in this change looks like an attack.
Part of CodeDelta · every compare mode · pointers for review, not verdicts
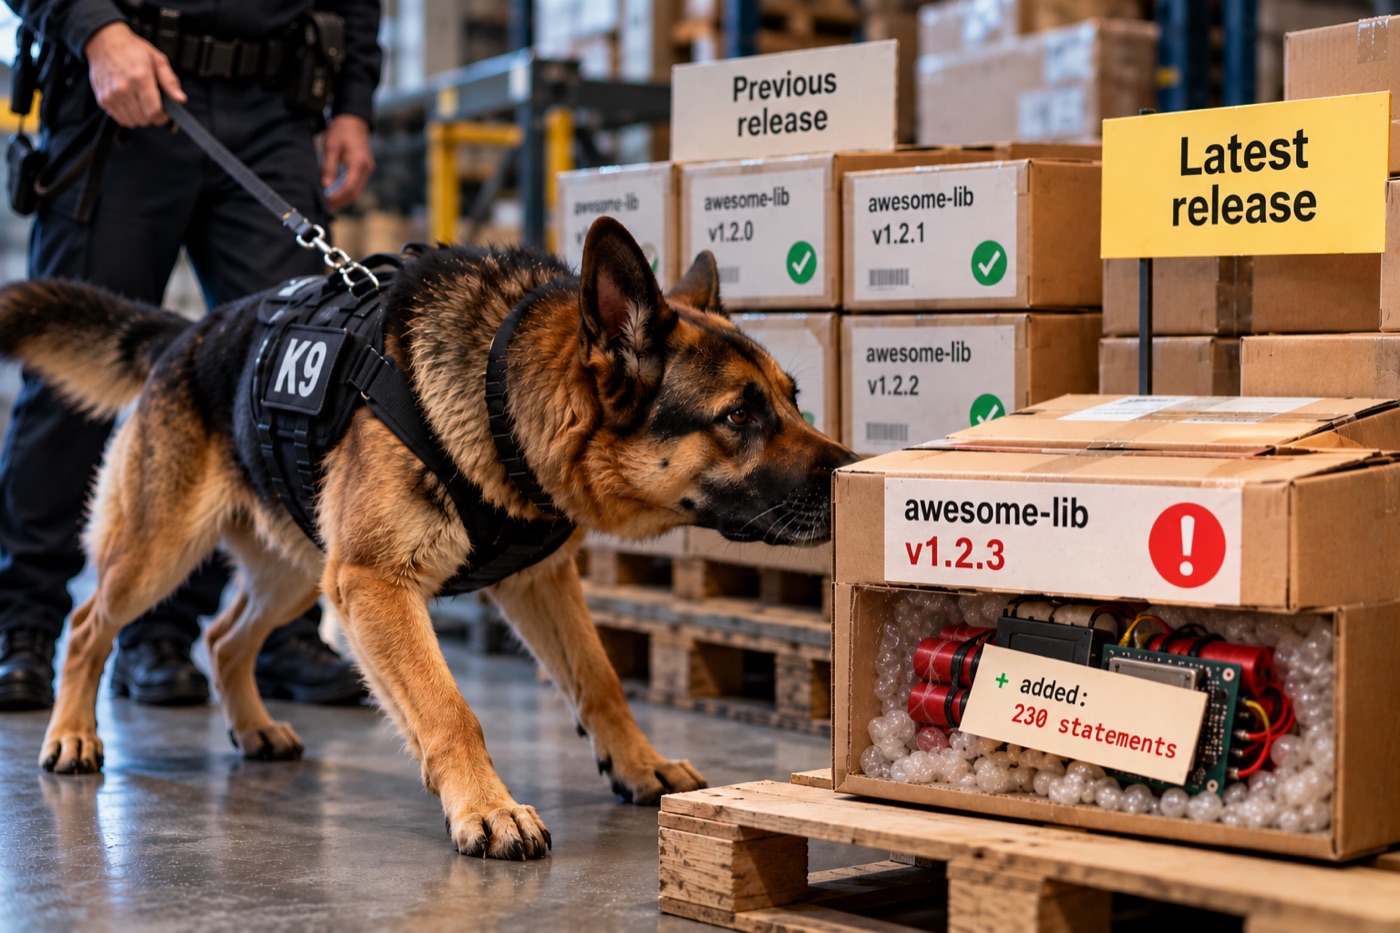
In September 2025 an attacker hijacked five npm libraries and appended the same single line, 76,438 bytes long, to each library’s main file. The rest of each release barely moved.
The Threat Index looks for that shape in every change you compare, so nobody has to know to look for it.
Try CodeDelta SEE THE REPORT →- Advisory: the same new code added to three or more files, or one very long new line.
- Attention: that code is obfuscated, decodes to a program, or the Agent Scan rates it HIGH; obfuscated code added to any file; or a large new file in an otherwise quiet release.
- Runs in Churn, Churn + Agent Scan and Both.
- Shows in its own report, at the top of the Agent Scan report, in the PR comment and in the app.
- Reports only. It never blocks a merge.
The report
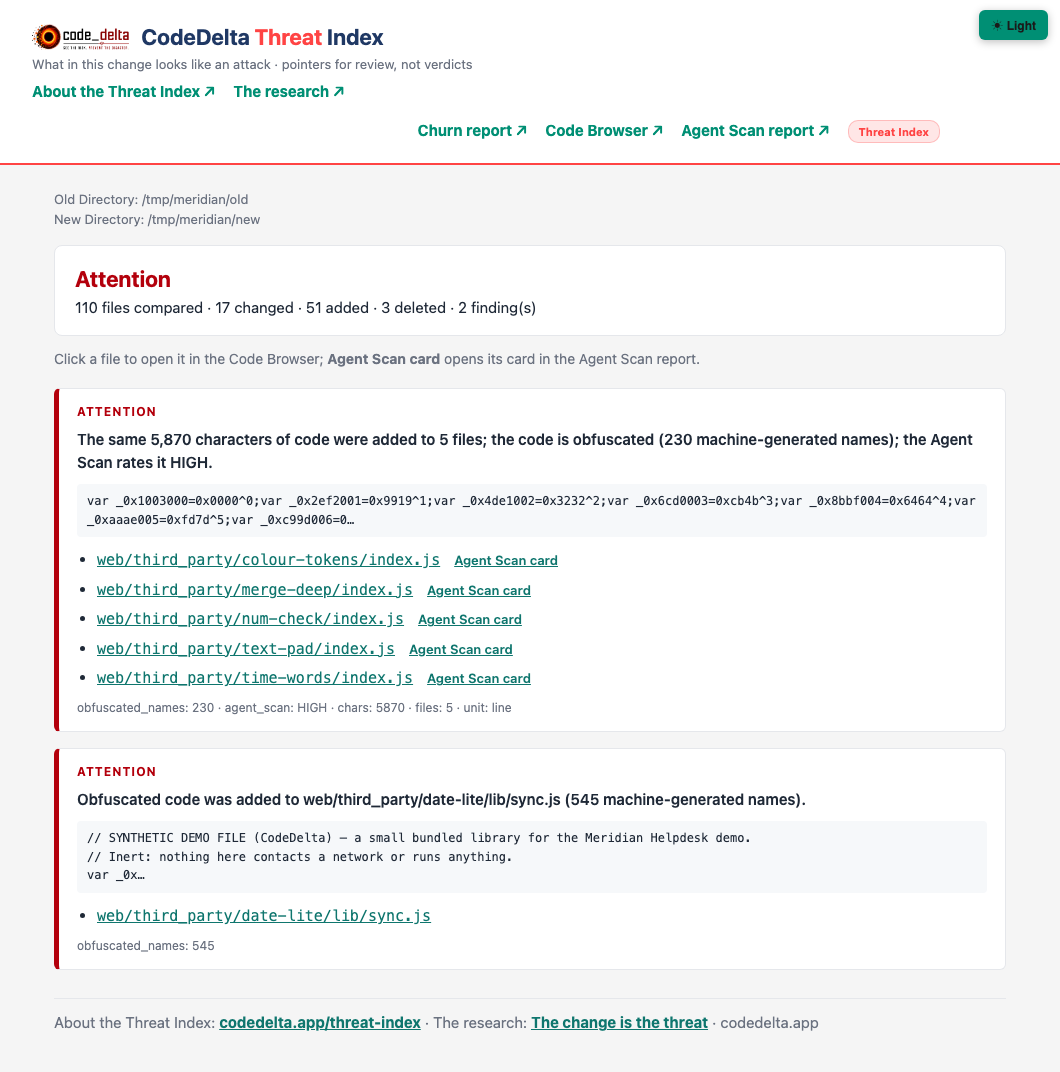
From the CodeDelta Churn + Agent Scan demo, which plants a dependency hijack in the shape of the September 2025 attack. The demo files are synthetic and inert. Run the demo in CodeDelta to see it yourself.
The research behind it
The change is the threat: 14 hijacked packages and why you scan what changed.